NoetixGRC Platform
A unified SaaS platform with 23 integrated modules and an agentic AI core, automating governance, risk, and compliance work that used to take weeks.
Six pillars. 23 modules. One AI core.
Every capability your organisation needs, orchestrated by AI agents that draft policies, gather evidence, surface risk, and brief the board, so your team focuses on judgement, not data entry.
Risk Management
AI-assisted risk identification and quantification, with agentic workflows that continuously refresh registers, heat maps, scenario models, exposure to outside suppliers, and vulnerability intelligence.
Compliance & Regulatory
AI agents map controls to frameworks, interpret regulatory change, and assemble evidence ready for audit across ISO 27001, PCI DSS, DORA, NIS2, GDPR, and the EU AI Act.
Audit & Assurance
Run internal audits with AI-guided scoping, automated evidence collection, intelligent sampling, and audit trails. Analysts review what matters, and agents handle the rest.
Incident & Response
Agentic detection, triage, and escalation with AI-generated root cause analysis, response playbooks, and post-incident reports drafted in minutes, not days.
Dashboards & Reporting
AI-curated executive narratives alongside operational dashboards updated in real time, with reports ready for the board, KRIs, trend analytics, and compliance scorecards generated on demand.
Platform & Integrations
An agentic backbone that connects your tech stack, orchestrates workflows across modules, and enforces controls based on role, with a Noetix Agent at your team's side.
Three stages. One agentic workflow.
From a regulatory prompt to a report ready for audit, with a human reviewer in control at every stage.
- 01Step 1
Drafts the policy
Noetix Agent interprets the framework requirement and drafts a tailored policy aligned to your organisation's context.
- 02Step 2
Collects the evidence
Agents query connected systems, attach artefacts, and map each control to the policy clause it satisfies.
- 03Step 3
Generates the report
A report ready for audit is assembled, with narrative, evidence index and gap analysis, for human review and sign-off.
Clear oversight. Connected governance.
Executive reporting, security operations and programme oversight, with a shared view of risk, control implementation and performance against targets.
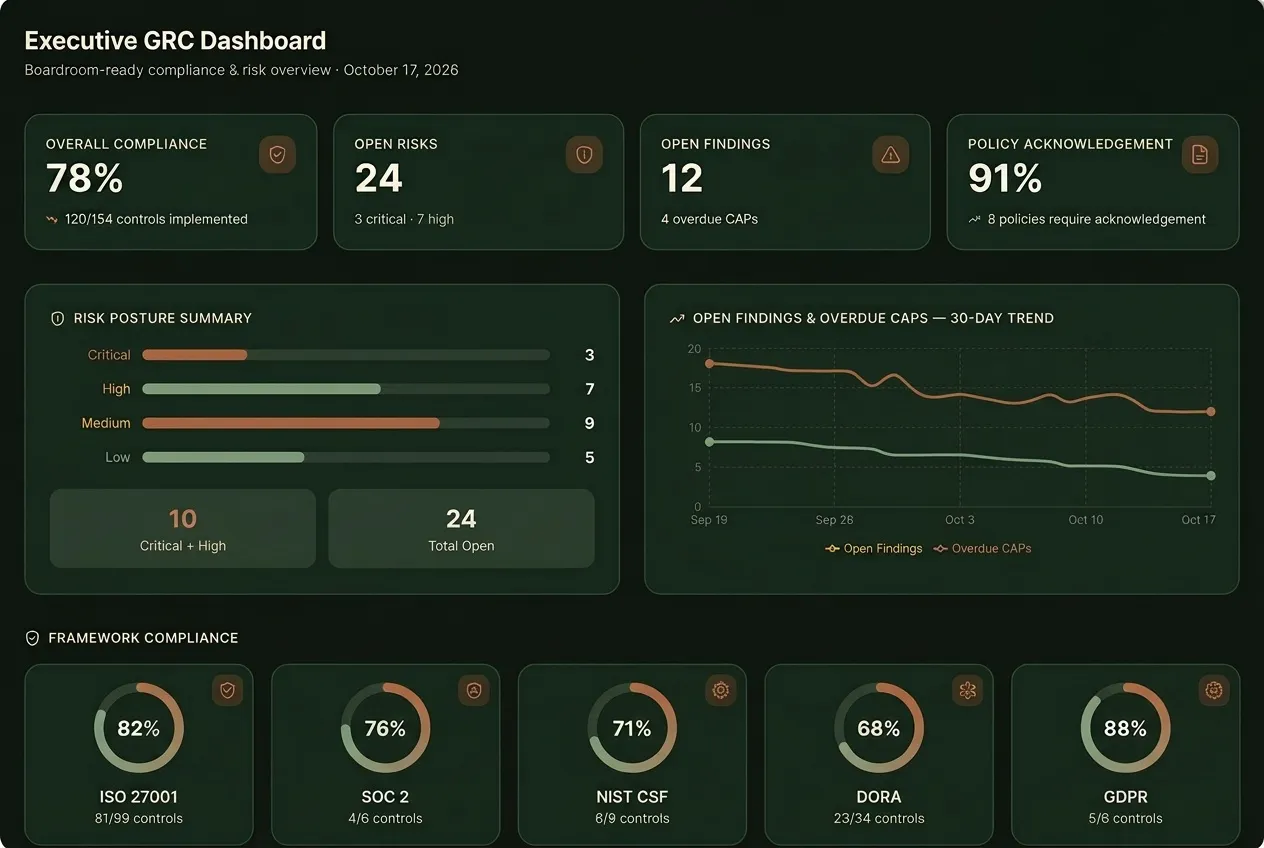
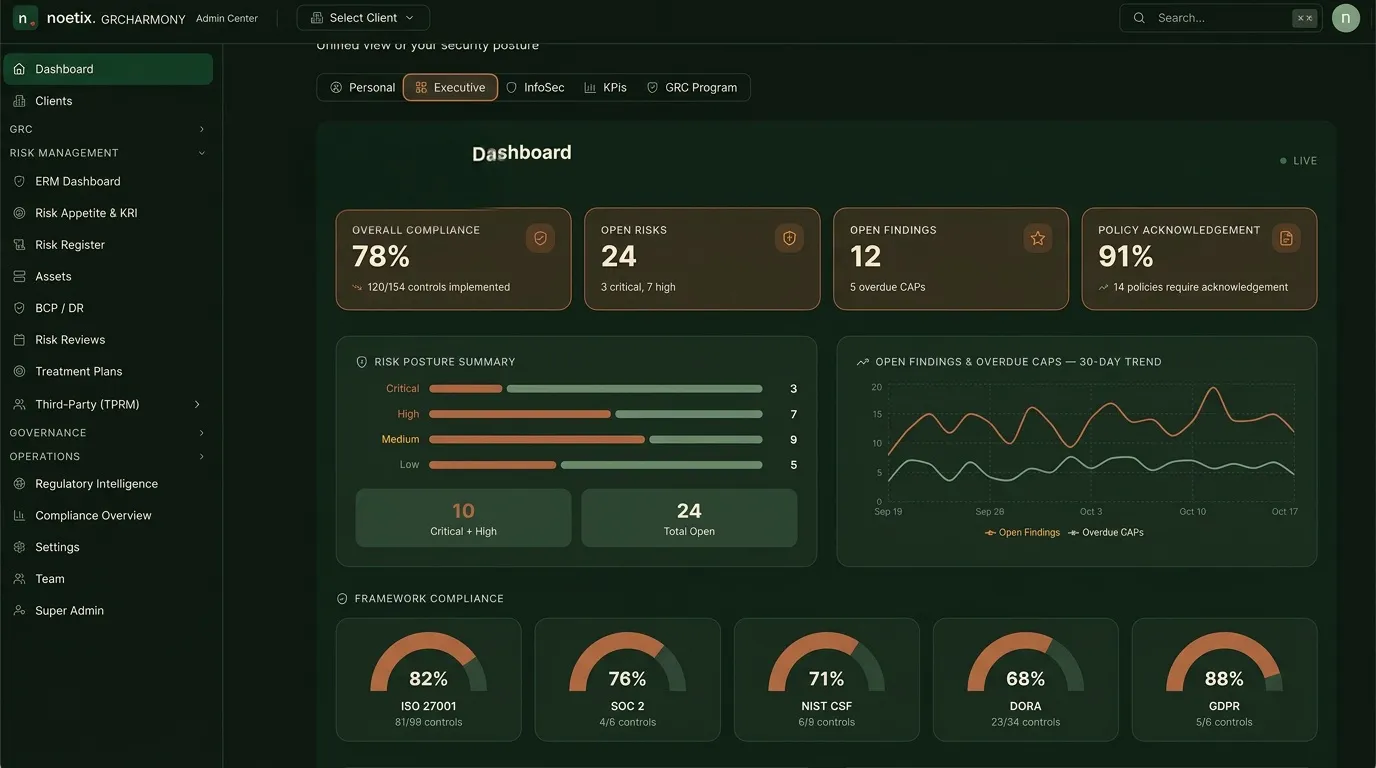
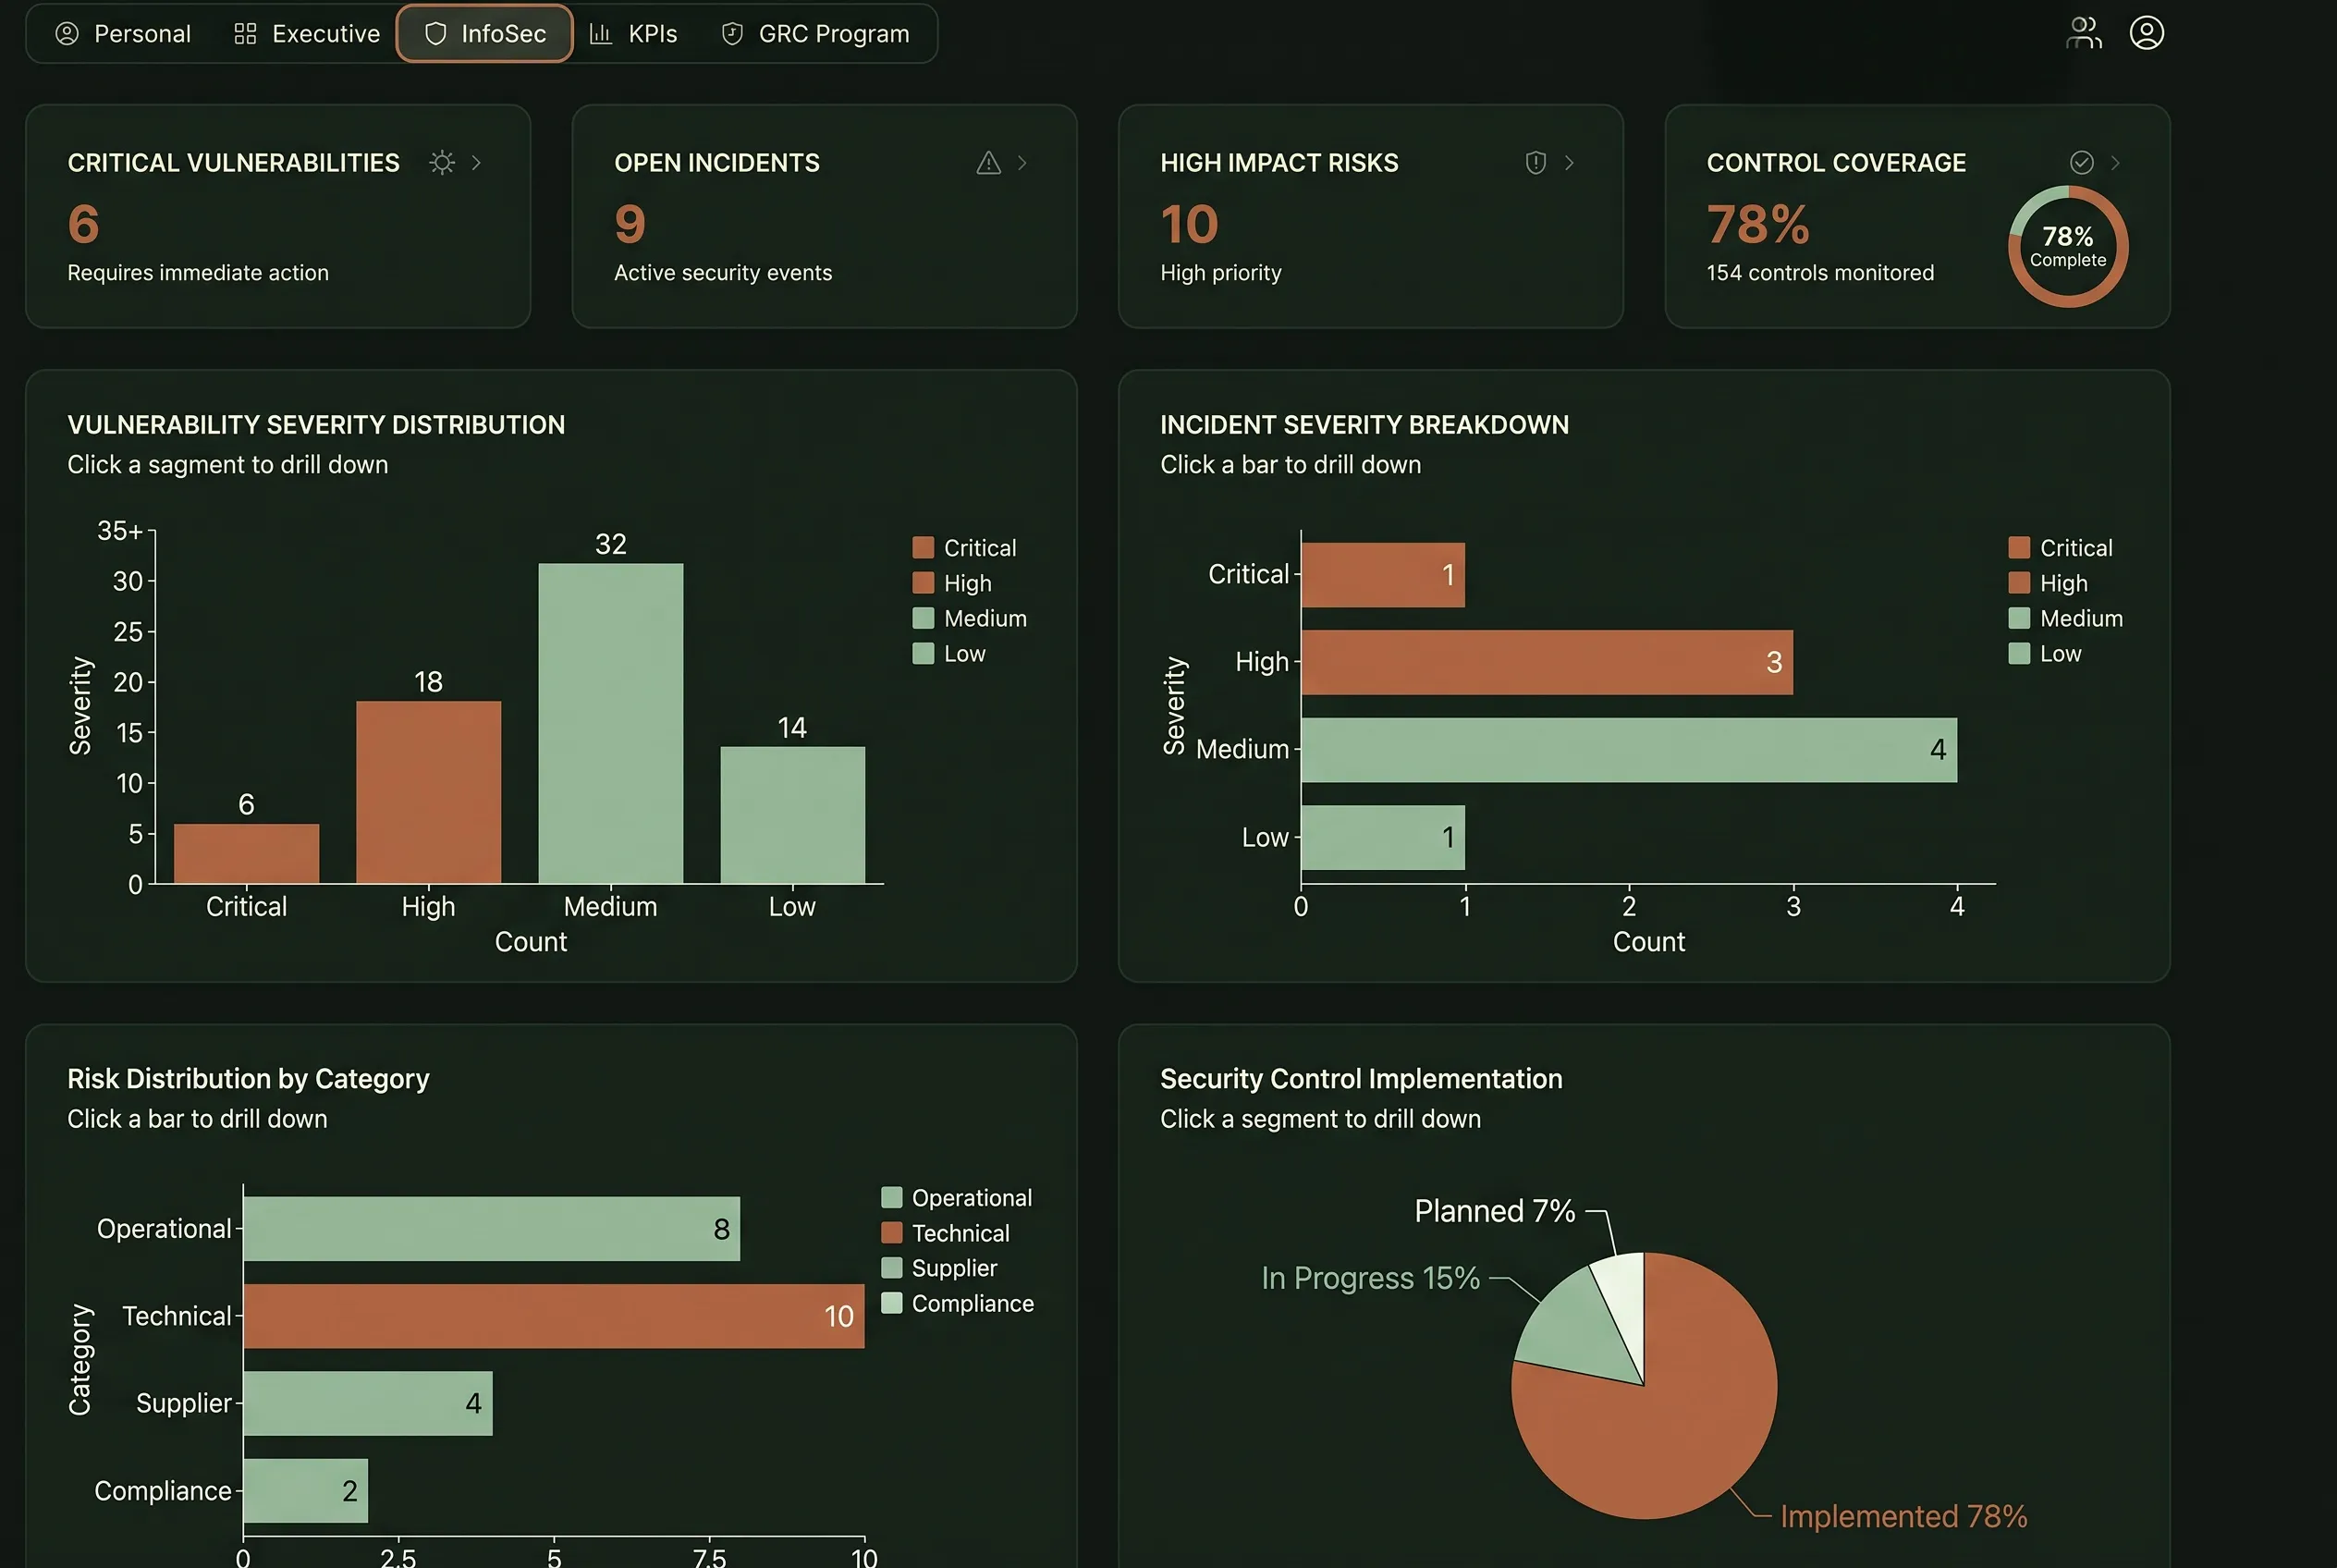
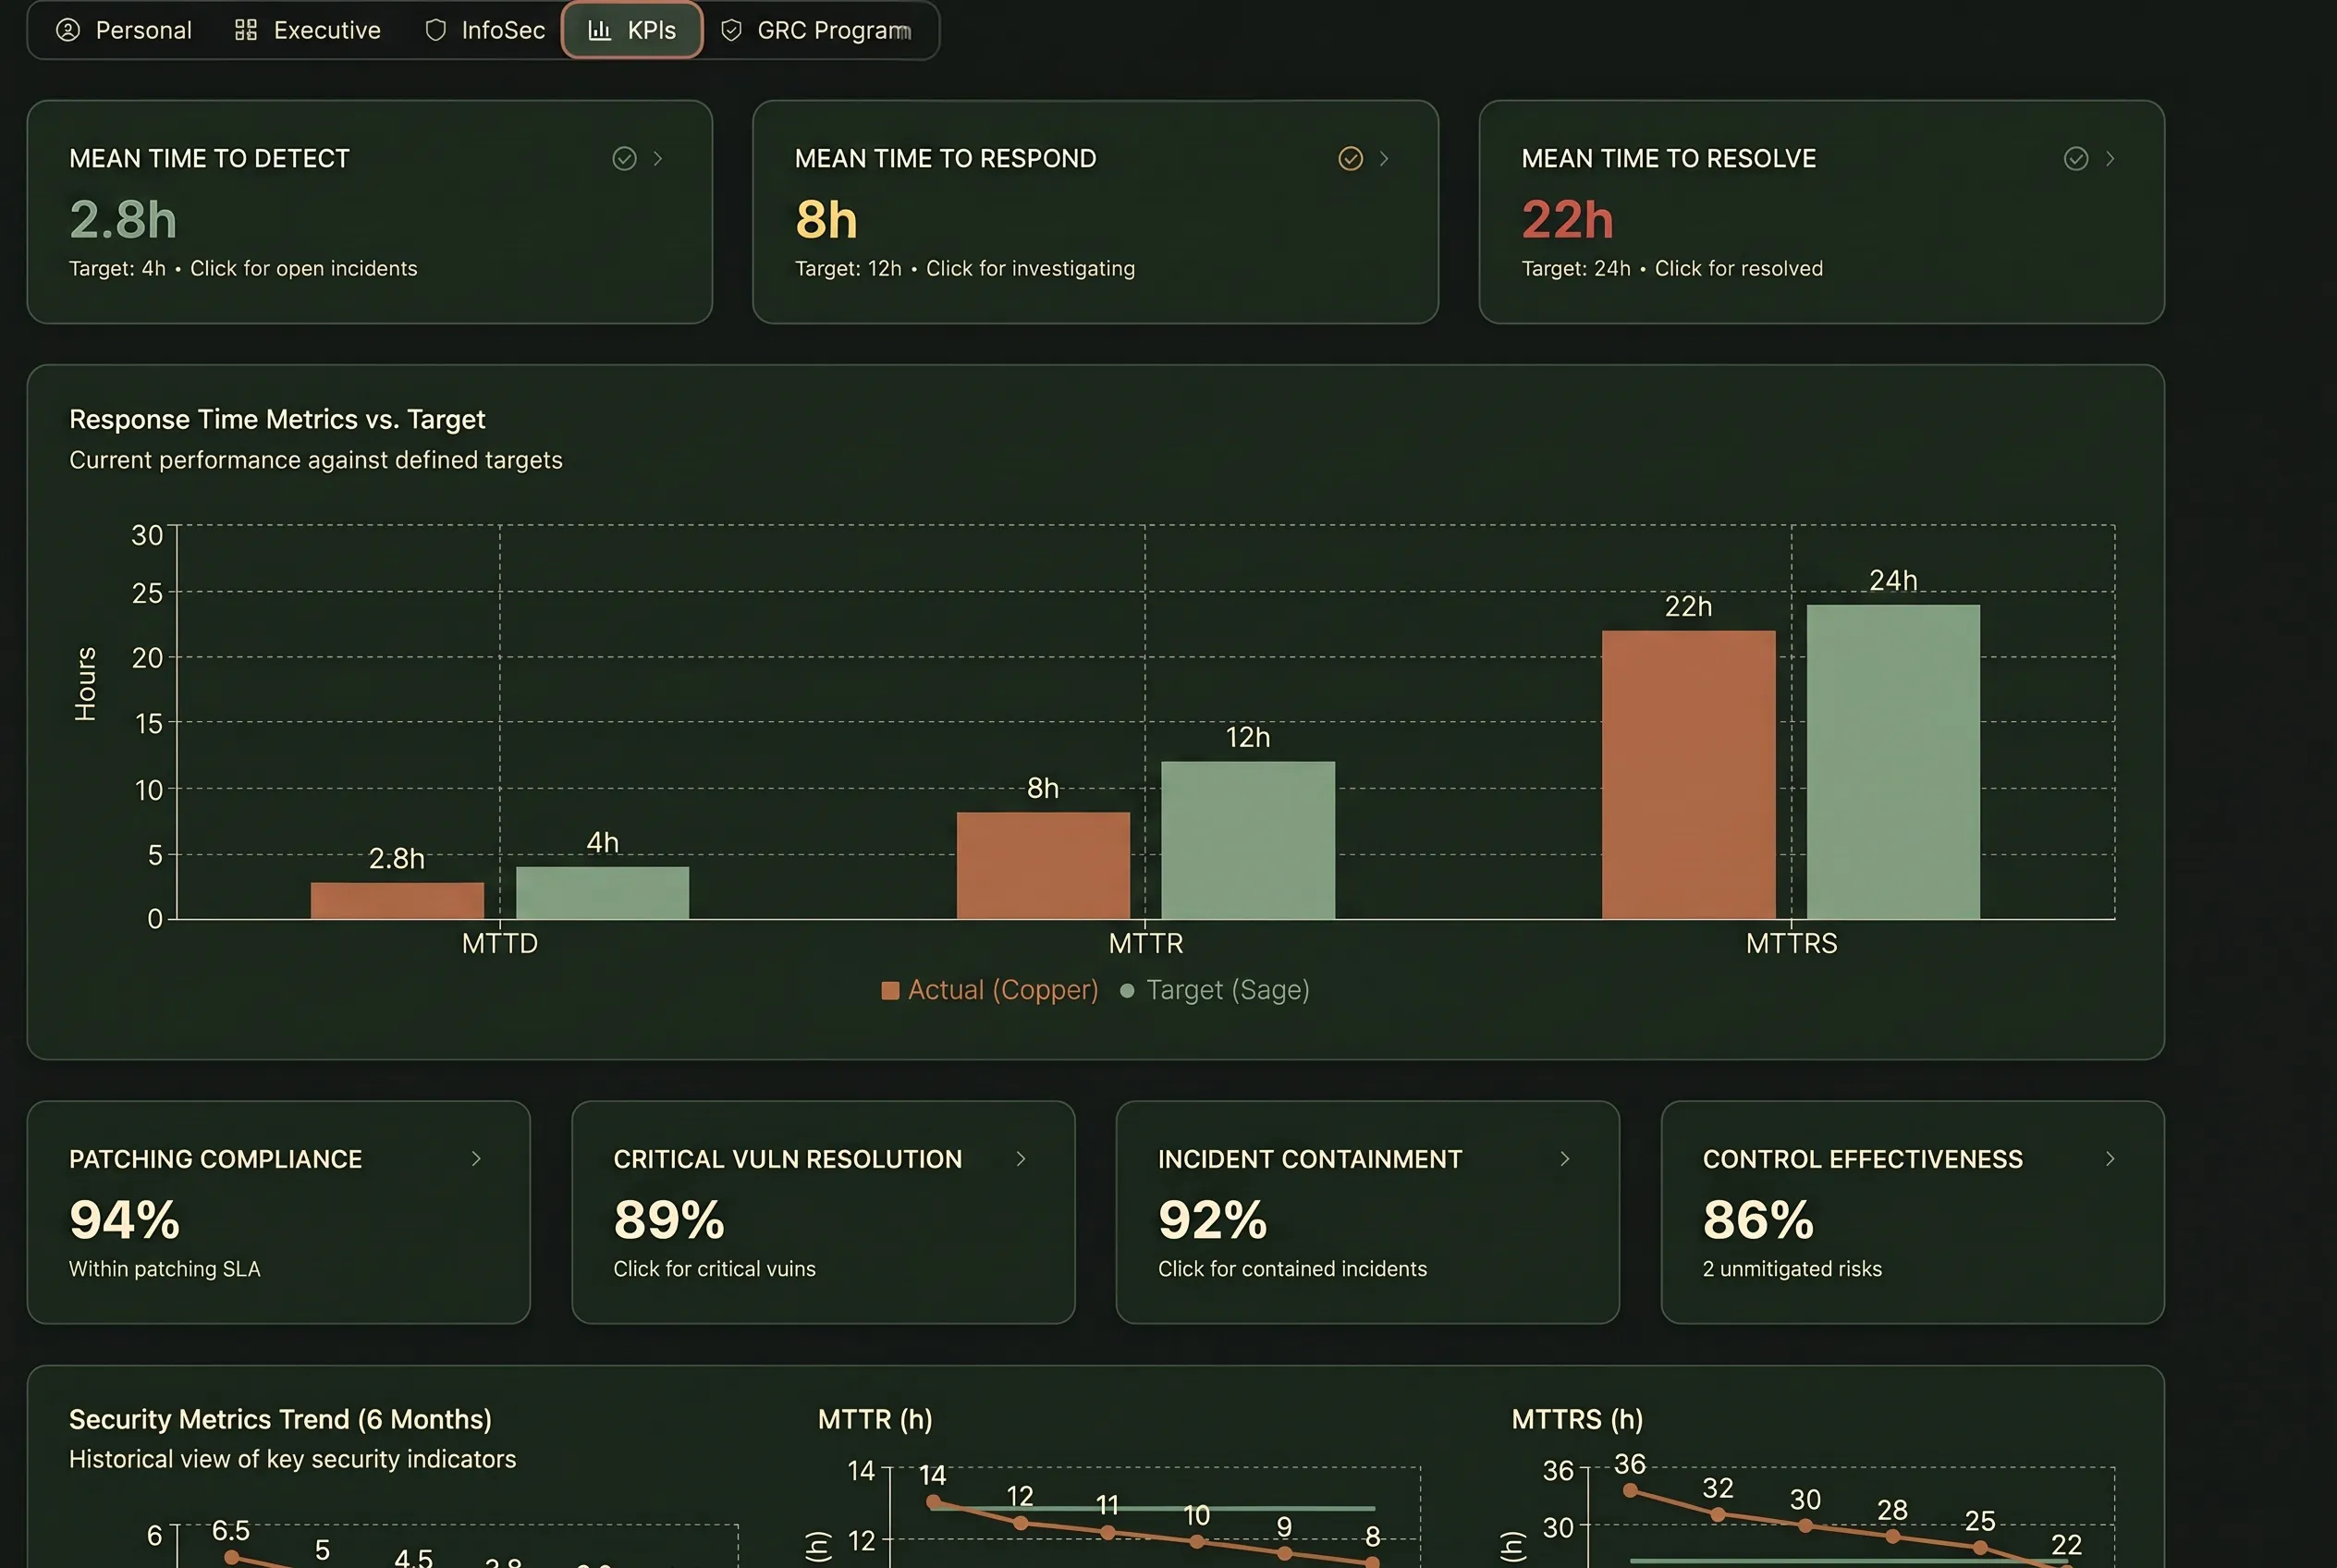
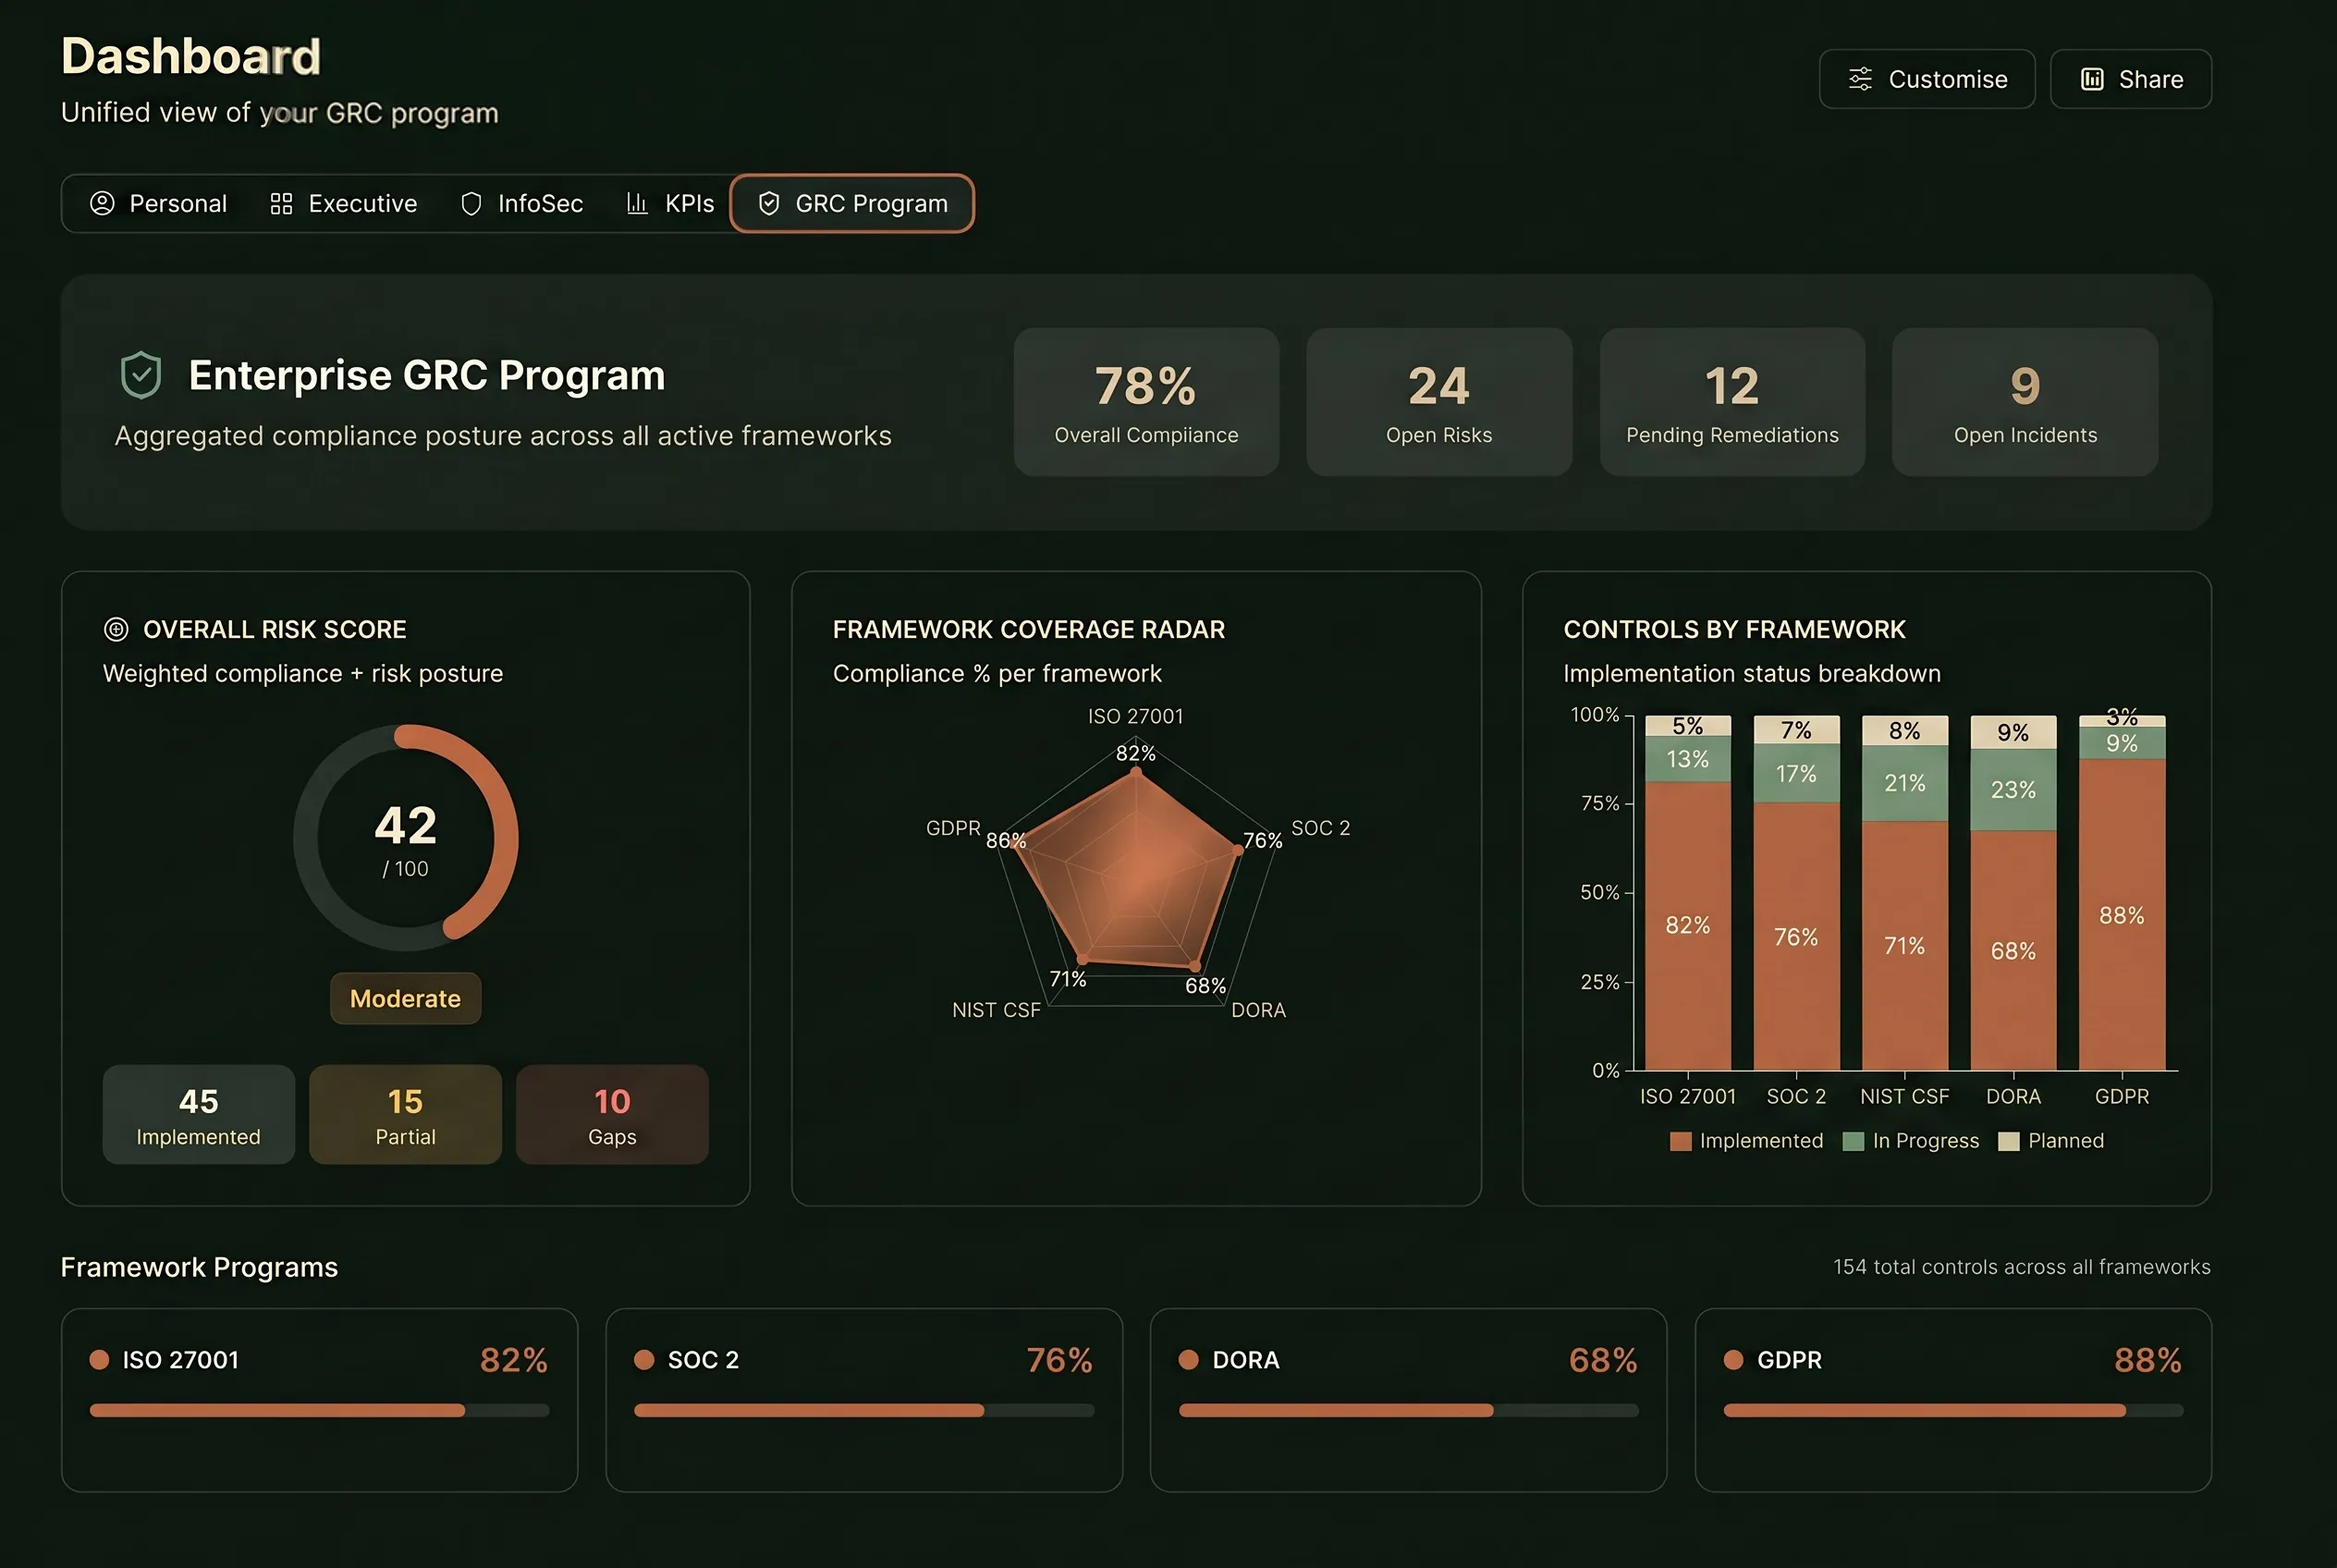
Product screens shown with illustrative data.
Try our free NIS2 Readiness Assessment
Get an indicative view of whether your organisation falls under the NIS2 Directive and assess your posture across 13 domains in about 15 minutes.
Ready to see NoetixGRC in action?
Book a personalised demo and discover how our platform can transform your governance, risk, and compliance operations.